
VPS Tutorials
Pangolin on a VPS (2026): Newt tunnels, HTTPS, authentication and backups
Self-host Pangolin on Ubuntu, connect private web services with Newt, configure Traefik HTTPS and identity rules, size transfer allowances and verify backup recovery and upgrades.
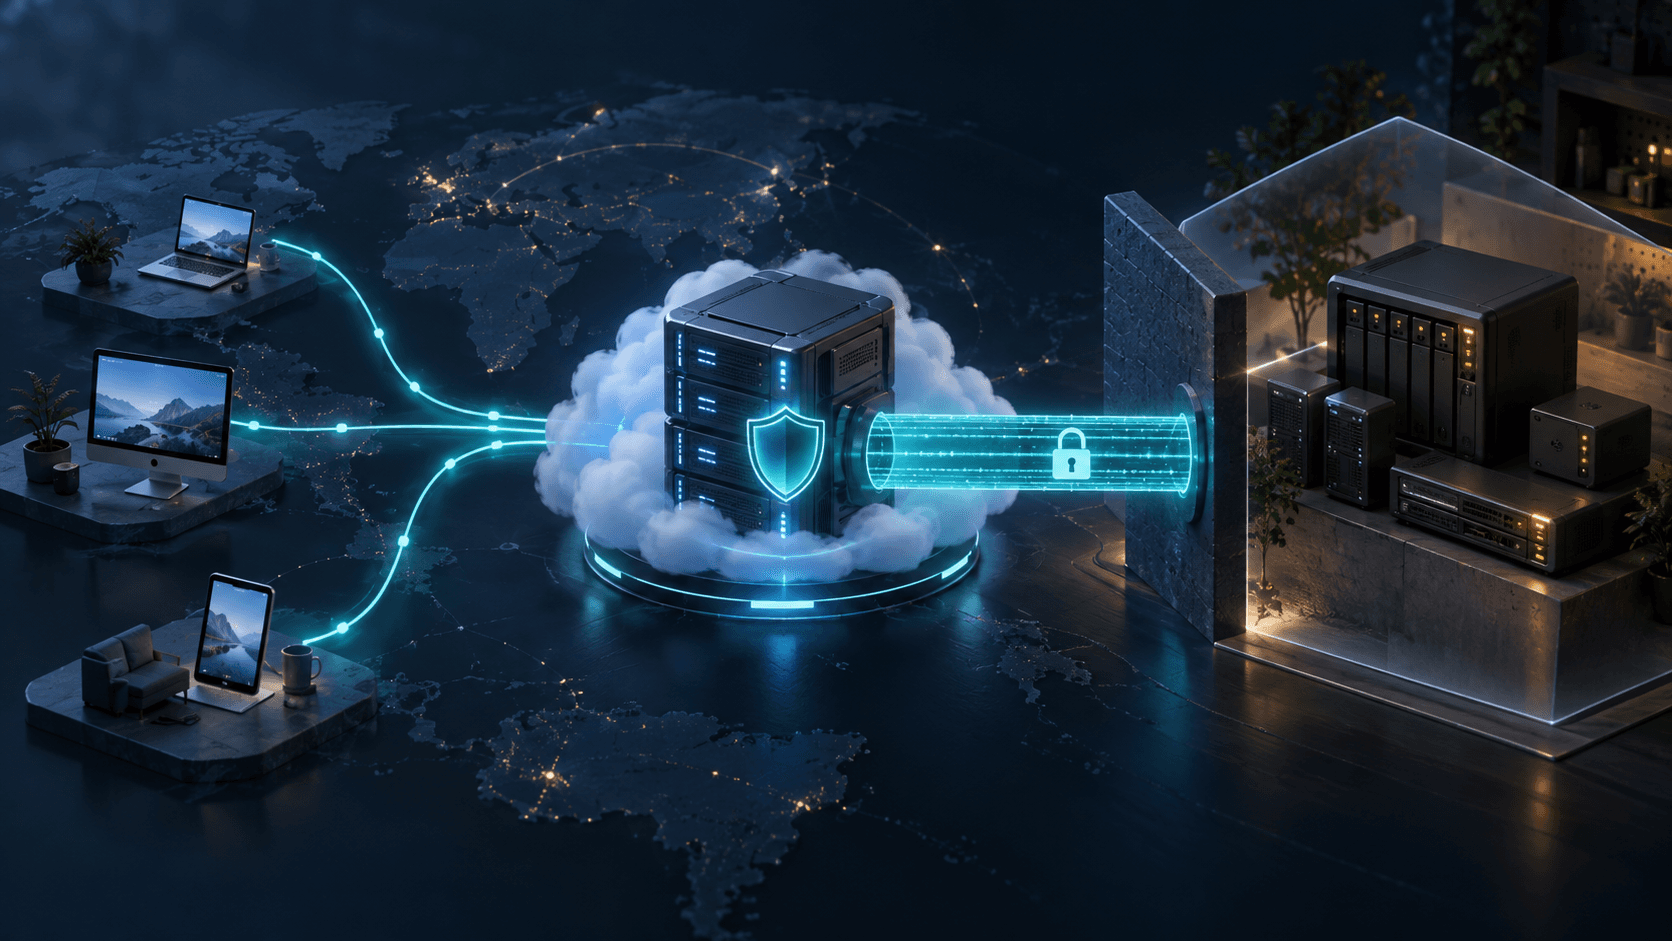
A home NAS, Home Assistant instance, photo library or development server may have no public IP. Pangolin combines reverse proxying, encrypted tunnels, domain certificates and identity-based access in a self-hosted dashboard. It provides a way to publish selected private web services without assembling FRP, a proxy, certificate automation and an authentication service separately.
This tutorial deploys Pangolin Community Edition on Ubuntu 24.04, connects a private network with standalone Newt, and covers Traefik HTTPS, users, access rules, traffic sizing, backups, upgrades and troubleshooting. The September 14, 2026 reference used Pangolin 1.22.2. The release check on November 16, 2026 found Pangolin 1.26.0 and Newt 1.20.0 as the latest stable releases. The downloaders select current releases, so the original version number does not pin installation. Record and review the actual server, connector and proxy versions before going live.
For public web resources, business traffic passes through the public VPS. Visitors reach Traefik/Pangolin there, and the VPS forwards requests through the Newt tunnel to the private service. Transfer allowance, sustained port speed, connectivity and server geography directly affect that path. Private-resource connections have their own connection modes; do not assume every Pangolin connection follows the public-resource path.
The VPS supplies the domain entry point, TLS, identity checks and access rules. Newt runs inside the private network and initiates an encrypted connection outward. The home connection therefore does not need public IPv4 or inbound application-port forwarding.
Typical uses include:
- HTTPS access to a NAS, photo service, Home Assistant or monitoring dashboard.
- Temporary access for colleagues or customers with authentication or an expiring link.
- Connecting sites in homes, offices and other cloud networks.
- Managing public web resources, private resources and their access policies centrally.
- Replacing a separately maintained FRP, Nginx, Certbot and Authelia stack.
Publishing a resource and creating a private device network are different uses. For device-to-device private access, see NetBird. For simple port forwarding with fewer components, see FRP. Pangolin also supports private access, but a public web resource is an internet-facing endpoint whose protection you must configure and test.
| Option | Control plane | Typical traffic path | HTTPS and identity | Suitable use |
|---|---|---|---|---|
| Pangolin | Self-hosted VPS | Visitor → VPS → Newt → private service | Integrated | Several web services, team access, temporary sharing |
| Cloudflare Tunnel | Cloudflare | Visitor → Cloudflare → tunnel | Available through its services | Avoid operating an entry VPS; accept third-party hosting |
| FRP | Self-hosted | Visitor → frps → frpc → backend | Configure separately | SSH, game ports, simple TCP/UDP forwarding |
| NetBird | Self-hosting available | Direct peers where possible; relay otherwise | Focuses on private-network identity/policies | Device networking and fine-grained private access |
Consider Cloudflare Tunnel when managed ingress suits the service and platform terms. Pangolin suits users who want to operate the VPS, domains and access platform themselves and can maintain the associated security, upgrades and backups.
The public-resource path is browser → public VPS running Traefik, Pangolin and Gerbil → encrypted tunnel → Newt host → LAN service. The diagram retains the same sequence:
浏览器
  ↓ HTTPS
公网 VPS:Traefik + Pangolin + Gerbil
  ↓ 加密隧道
Newt 所在内网机器
  ↓ LAN
NAS / Home Assistant / 内网站点
For a 10 GB download, the VPS receives approximately that data from the tunnel and sends it to the visitor, plus protocol overhead. An outbound-only allowance is roughly charged for the download's outbound leg; a bidirectional allowance can count roughly both legs. Confirm billing direction, overage prices and sustained port limits with the provider.
| Sustained rate | Theoretical data in 30 days | Practical implication |
|---|---|---|
| 1 Mbps | About 324 GB | Light dashboards and occasional photos |
| 5 Mbps | About 1.62 TB | Frequent files or several visitors need headroom |
| 10 Mbps | About 3.24 TB | Video, backup traffic and large downloads consume allowances |
| 100 Mbps | About 32.4 TB | Far beyond many small metered plans |
The reference formula is Mbps × 1,000,000 ÷ 8 × 2,592,000 秒: Mbps × 1,000,000 bits/second ÷ 8 × 2,592,000 seconds. These are decimal totals at continuous full utilization for 30 days, before TLS, tunnel overhead, retransmissions and peaks. They are not measured provider performance.
The older baseline described 1 vCPU/1 GB/8 GB SSD as a minimum. The current VPS guide describes 1 vCPU/2 GB/8 GB SSD as a basic deployment, warning that 1 GB systems may need swap during installation, updates or traffic spikes. Its recommended resources remain 2 vCPU/2 GB/20 GB SSD. Treat 1 GB as a constrained test, not a production guarantee.
| Use | Suggested starting VPS | Main concern |
|---|---|---|
| Personal, 2–5 light web services | 2 cores, 2 GB, 20 GB SSD, 1 TB/month | Reliability and sufficient transfer |
| Photos and file sharing | 2–4 cores, 2–4 GB, 3 TB+ transfer | Sustained port speed and outbound billing |
| Small team | 4 GB+ and adequate SSD | Concurrent users, logs and update space |
| Streaming or sustained backups | High-transfer plan sized to workload | Calculate monthly usage and overage exposure |
Choose geography with both legs in mind: visitor to VPS and VPS to the home connection. Asian visitors reaching an Asian home service through a European VPS create a detour; the same principle applies to any regions. These are workload estimates, not a promise of latency or provider capacity.
Examples use:
- Base domain
example.com. - Dashboard
pangolin.example.com. - Public resource
nas.example.com. - Documentation IPv4
203.0.113.10. - Installation directory
/opt/pangolin.
Replace these with your real values. Wildcard DNS lets new subdomains resolve without adding records individually:
Type: A
Name: *
Value: 203.0.113.10
Proxy: DNS only
Alternatively, create separate records for pangolin.example.com and nas.example.com. Add AAAA only with working VPS IPv6. Wildcard DNS does not create a wildcard TLS certificate: default HTTP validation issues certificates for actual hostnames; wildcard certificates require suitable DNS validation and protected DNS credentials.
Check DNS and bindings:
dig +short A pangolin.example.com
dig +short A nas.example.com

sudo ss -lntup | grep -E ':(22|80|443|51820|21820)\b' || true
Install dnsutils if dig is missing. Default ports are:
80/TCP: HTTP redirects and default ACME domain validation.443/TCP: Dashboard and HTTPS resources.51820/UDP: site tunnels, including Newt.21820/UDP: relayed client tunnels.22/TCP: SSH, restricted to administrator addresses.
21820/UDP is required for the client feature, not every public-Newt web deployment. The reference firewall includes it to follow the full quickstart. If you do not use clients, review actual mappings and close the unused public port. Custom tunnel ports must match the generated configuration and firewall.
On Ubuntu 24.04:
sudo apt update
sudo apt upgrade -y
sudo apt install -y ca-certificates curl jq docker.io docker-compose-v2
sudo systemctl enable --now docker
sudo usermod -aG docker "$USER"
Log out and back in for Docker-group membership; it effectively grants root-level control. Ensure less, openssl and dnsutils are available for review/TLS/DNS checks, and netcat-openbsd for the later nc test. Verify:
docker version
docker compose version
docker run --rm hello-world
Use docker compose, not legacy docker-compose. Resolve existing Nginx, Caddy or Traefik ownership of 80/443 before installing. If a separately managed conventional proxy is your requirement, see Nginx Proxy Manager; two proxies cannot bind the same host ports.
Set provider rules first: 80/TCP, 443/TCP, 51820/UDP, and 21820/UDP when clients are used, with SSH from your management address only. The full quickstart rules are:
sudo ufw default deny incoming
sudo ufw default allow outgoing
sudo ufw allow from YOUR_ADMIN_IP to any port 22 proto tcp
sudo ufw allow 80/tcp
sudo ufw allow 443/tcp
sudo ufw allow 51820/udp
sudo ufw allow 21820/udp
sudo ufw enable
sudo ufw status numbered
Replace YOUR_ADMIN_IP before enabling UFW. Keep the active SSH connection and provider console available. If locked out, follow the UFW recovery checklist.
Docker manages forwarding rules independently. Check docker compose ps, ss, provider policy and an external scan rather than assuming UFW hides unintended published ports. The VPS is now part of the private services' security boundary.
The quickstart recommends Ubuntu 20.04+ or Debian 11+ and supports Linux amd64/arm64. Download and inspect the bootstrap script in a clean directory. Run the commands individually: after the bootstrap downloads the installer, verify the binary against the selected official release asset before the final sudo command:
sudo install -d -m 0750 -o "$USER" -g "$USER" /opt/pangolin
cd /opt/pangolin

curl -fsSLo get-installer.sh \
  https://static.pangolin.net/get-installer.sh
less get-installer.sh
bash ./get-installer.sh
sudo ./installer
The downloaded script fetches the latest release's installer binary. Reviewing the script alone does not verify that binary; compare its digest with the selected official release asset before the privileged installer step, using published checksums where available. Do not treat the September version as a pin or rerun installation over an existing stack as an upgrade method.
All deployment files go in the current directory, so enter /opt/pangolin first. Choose:
- Edition
Community. - Base domain
example.com. - Dashboard
pangolin.example.com. - A maintained Let's Encrypt/admin email address.
- Gerbil tunneling enabled.
- SMTP skipped initially if it is not ready.
Inspect actual services and image references after generation:
cd /opt/pangolin
docker compose config --services
docker compose config --images
docker compose ps
Record Pangolin, Gerbil, Traefik and the Badger plugin version. If an image uses latest, select an explicit tested tag/digest before public use. Related component versions do not share one version number. docker compose config --quiet checks parsing, not health:
docker compose config --quiet
docker compose logs --tail=150
The historical setup URL may look like:
https://pangolin.example.com/auth/initial-setup?token=ONE_TIME_TOKEN
Current quickstart instructions open the initial-setup page and ask for the token printed by the installer or Pangolin container logs. Use the actual output for your release instead of assuming the token is always a query parameter. Keep both setup tokens and token-bearing URLs private; container logs can contain this initial credential.
Complete setup promptly from a trusted computer, create the administrator, then create the first organization before adding a Site. Check:
- The dashboard opens with valid HTTPS.
- The certificate matches
pangolin.example.com. - The administrator has a unique strong password.
- Daily access uses a separate ordinary account.
- A tested emergency administrator remains available before adding external identity.
Check TLS and headers:
curl -I https://pangolin.example.com
openssl s_client \
  -connect pangolin.example.com:443 \
  -servername pangolin.example.com </dev/null 2>/dev/null \
  | openssl x509 -noout -subject -issuer -dates
Do not enter credentials through an unresolved certificate warning; fix DNS and certificate issuance first.
A Site represents a reachable private location: home, office or another cloud. Create it in your organization and copy its Newt ID, Secret and Endpoint. Use a stable, always-on Linux host that can reach the backend; it need not be the NAS itself.
Current documentation recommends Pangolin CLI for new Sites, while standalone Newt remains supported as the smaller connector. This tutorial keeps the Newt/systemd method. Follow the Newt-specific instructions if the general Site page shows the newer CLI. Newt uses NEWT_ID/NEWT_SECRET; do not copy the CLI's SITE_ID/SITE_SECRET settings into this service.
Download and inspect Newt's installer:
curl -fsSLo get-newt.sh https://static.pangolin.net/get-newt.sh
less get-newt.sh
sudo bash ./get-newt.sh
rm -f get-newt.sh
It also selects a current release. Check release notes, downloaded-artifact verification messages and compatibility with your server before updating an older installation. A skipped checksum check is not verification. Confirm the binary actually exists at /usr/local/bin/newt before enabling the unit; adjust ExecStart if you deliberately installed elsewhere.
Create the private environment file:
sudo install -d -m 0700 /etc/newt
sudo install -m 0600 /dev/null /etc/newt/newt.env
sudoedit /etc/newt/newt.env
Fill in real Site credentials:
NEWT_ID=REPLACE_WITH_SITE_ID
NEWT_SECRET=REPLACE_WITH_SITE_SECRET
PANGOLIN_ENDPOINT=https://pangolin.example.com
Keep the secret out of repositories, screenshots and literal shell commands. Create the unit:
sudoedit /etc/systemd/system/newt.service
Use:
[Unit]
Description=Pangolin Newt Tunnel Client
Wants=network-online.target
After=network-online.target

[Service]
Type=simple
User=root
Group=root
EnvironmentFile=/etc/newt/newt.env
ExecStart=/usr/local/bin/newt
Restart=always
RestartSec=2
UMask=0077
PrivateTmp=true

[Install]
WantedBy=multi-user.target
Newt reads those variables automatically; they need not be repeated as process arguments. The example runs as root, so restrict who can modify the binary, service and environment file. Start it:
sudo systemctl daemon-reload
sudo systemctl enable --now newt
sudo systemctl status newt --no-pager
sudo journalctl -u newt -n 100 --no-pager
Confirm the Site is online in the dashboard. Outbound establishment normally avoids home router inbound mappings, but the home network must allow HTTPS to the Endpoint and the configured UDP tunnel ports. Restart Newt after changing its environment file.
Suppose NAS 192.168.1.20:5000 should be reachable at nas.example.com. Create:
Resource type: Public
Domain: nas.example.com
Site: Home
Target hostname/IP: 192.168.1.20
Target port: 5000
Target method: HTTP
Target is the address reachable from the Newt host, not necessarily from the VPS. localhost means the connector's own network namespace; it is valid only if the intended backend really runs there. It does not automatically mean a different NAS or another container.
The backend protocol is independent of public TLS. Use HTTP for this HTTP target, HTTPS for a genuinely HTTPS target with appropriate certificate validation. Do not disable upstream verification just to hide a wrong scheme or certificate. Check app-specific trusted-proxy and WebSocket requirements without allowing arbitrary identity headers from untrusted sources.
From the Newt host:
curl -I http://192.168.1.20:5000
nc -vz 192.168.1.20 5000
From an external network:
curl -I https://nas.example.com
A protected resource may redirect to login; that is different from a tunnel error. Some backends reject HEAD even when GET works. Test the actual application in a browser, preferably using mobile data initially to avoid home NAT-loopback confusion.
Public HTTP resources have Platform SSO enabled by default according to current documentation, but verify the actual resource or inherited policy. A hard-to-guess domain does not protect NAS administration, Home Assistant or development interfaces.
- Keep platform authentication enabled.
- Assign only the users/roles that need the resource.
- Give temporary visitors an expiring Share Link or an appropriate one-time method.
- Revoke sharing when finished.
- Review stale users, roles and resources regularly.
Share Links and their access tokens are bearer credentials: holders can use them without a Pangolin user login. They are not automatically single-use, and Never expire remains valid until revoked. Set expiry deliberately and test deletion/expiration. Link-based access does not provide the upstream app with per-user identity headers.
Rules are processed by configured priority from top to bottom. Allow/Bypass Auth skips authentication; Deny blocks the request; Pass to Auth continues to identity/PIN/password checks. Test with an ordinary permitted user, an unauthorized user and a logged-out browser. Do not retain broad bypass rules created during troubleshooting. See access rules and public-resource authentication.
Browser authentication does not protect an arbitrary bare TCP/UDP port in the same way. Prefer Private Resources or NetBird/WireGuard for administrative SSH and databases, with native protocol authentication and deliberate source restrictions. Review game-port latency, UDP and transfer separately. Feature availability and identity-provider support should be checked against the deployed release and edition.
SMTP serves invitations, notifications and account flows, but is optional for the initial tunnel test. First establish dashboard login → Site online → healthy Newt logs → test resource access → enforced authentication → recoverable backup:
Dashboard 可登录
→ Site 在线
→ Newt 日志正常
→ 一个测试资源可访问
→ 身份认证生效
→ 备份可恢复
Then add SMTP and OIDC or another supported identity provider. Separate stages make DNS, cookies, callback, mail and tunnel failures easier to diagnose. Email OTP requires working mail delivery; it is not a substitute for configuring SMTP.
Use callback URLs matching the actual public hostname and HTTPS scheme. Preserve Host and X-Forwarded-Proto correctly through trusted proxies. Keep a local administrator session, then test the changed login path in a private window before ending it.
Save config plus docker-compose.yml, actual image identities, plugin settings and any other deployment files. Inspect paths first:
cd /opt/pangolin
find . -maxdepth 2 -type f -printf '%P\n' | sort
docker compose config --images
The compact backup below stops the stack and illustrates the core files. Its restart is not protected against an interrupted copy, and it does not cover every custom mount. Use the complete procedure that follows for the default installation.
cd /opt/pangolin
sudo docker compose down

sudo tar \
  --numeric-owner \
  -czf "/root/pangolin-backup-$(date +%F-%H%M%S).tar.gz" \
  config docker-compose.yml

sudo docker compose up -d
docker compose ps
Include .env, extra Compose files and certificate paths when used; do not indiscriminately archive all of /opt. Keep database, secrets, SMTP passwords and tokens private. The simple permissions/checksum commands are:
sudo chmod 600 /root/pangolin-backup-*.tar.gz
sudo sha256sum /root/pangolin-backup-*.tar.gz
For the default single-file quickstart, this root-run procedure saves consistent stopped configuration/data, image and mount identities, internal checksums and an archive checksum. It attempts to restart the previously running services even if the copy fails:
sudo bash <<'BACKUP'
set -Eeuo pipefail
umask 077
cd /opt/pangolin
compose=(docker compose -f docker-compose.yml)
mapfile -t running_services < <("${compose[@]}" ps --status running --services)
test "${#running_services[@]}" -gt 0
mapfile -t container_ids < <("${compose[@]}" ps -a -q)
test "${#container_ids[@]}" -gt 0
install -d -m 0700 /var/backups/pangolin
backup_dir=$(mktemp -d "/var/backups/pangolin/$(date -u +%Y%m%dT%H%M%SZ)-XXXXXX")
docker inspect --format '{{.Name}} {{.Config.Image}} {{.Image}}' "${container_ids[@]}" > "$backup_dir/images.txt"
docker inspect --format '{{.Name}} {{json .Mounts}}' "${container_ids[@]}" > "$backup_dir/mounts.txt"
resume_stack() { "${compose[@]}" start "${running_services[@]}" >/dev/null || true; }
trap resume_stack EXIT
"${compose[@]}" stop
cp -a config docker-compose.yml "$backup_dir/"
if test -f .env; then cp -p .env "$backup_dir/"; fi
(cd "$backup_dir" && find . -type f ! -name SHA256SUMS -print0 | sort -z | xargs -0 sha256sum > SHA256SUMS && sha256sum -c SHA256SUMS)
archive="$backup_dir.tar.gz"
tar --numeric-owner -C /var/backups/pangolin -czf "$archive" "$(basename "$backup_dir")"
tar -tzf "$archive" >/dev/null
(cd /var/backups/pangolin && sha256sum "$(basename "$archive")" > "$(basename "$archive").sha256")
printf 'Backup archive: %s\n' "$archive"
BACKUP
Freeze administrative changes during backup. If you use other project names, overrides, external databases or volumes outside config, adapt the Compose invocation and include their consistent backup before packaging. Saving a mount listing does not copy a named volume. Check container health after the restart attempt. Keep extra database/certificate backups with the same recovery set.
Back up the Newt host separately: /etc/newt/newt.env, /etc/systemd/system/newt.service and its binary/version identity. Encrypt the server archive and connector secrets, then copy them and checksums offsite. A local or automatic pre-migration SQLite copy does not replace an independent backup.
In an isolated restore drill, verify the archive checksum, extract it and verify SHA256SUMS from the extracted directory. Restore matching Compose/configuration, keys, certificates, complete data and any separate stores; use the recorded component versions and proper file ownership. Run the parsing check, start the isolated stack, verify login/organization/resource records and a controlled tunnel test. Avoid a competing production domain/identity until recovery is intentionally cut over.
Version 1.22 introduced features and migration requirements; later releases also need review. docker compose pull alone does not select a new version when image tags are fixed. The abbreviated maintenance sequence is:
cd /opt/pangolin

sudo docker compose down
sudo cp -a config "config.before-upgrade-$(date +%F-%H%M%S)"
sudo cp -a docker-compose.yml \
  "docker-compose.yml.before-upgrade-$(date +%F-%H%M%S)"

sudo docker compose pull
sudo docker compose up -d
sudo docker compose ps
sudo docker compose logs --tail=200
Before using it:
- Make and verify the full private/offsite recovery set from the previous section.
- Read the target release notes and review a compatible Pangolin, Gerbil, Traefik/Badger and connector combination.
- Update the selected image tags/digests and, where required, Badger's version in the actual Traefik config before the pull step. Keep the pre-edit configuration in the private backup.
- Follow required incremental upgrades and migration instructions, then pull and restart during a planned outage.
- Check logs and all relevant access paths before accepting the upgrade.
Pangolin runs migrations automatically and a failed database migration can block startup. Automatic SQLite pre-migration copies are useful but do not include every recovery component. For 1.22 AI Gateway use specifically, the release required Badger v1.6.0+, Gerbil 1.5.0 for private gateways and compatible clients; those historical requirements are not a current version prescription for every installation. Automatic config editing can be skipped with customized paths, and Gerbil is not automatically upgraded by the database migration.
Verify:
- Dashboard login works.
- Site/Newt reconnects.
- Resource HTTPS and actual app access work.
- Unauthorized users remain blocked.
- Share-link expiration and revocation work.
- Backup files are outside public web roots.
If migrations changed the schema, replacing one image with an older tag may fail. Restore the complete pre-upgrade configuration/data set with matching versions when rollback is needed.
A 502 does not prove the entire tunnel is working; it commonly means an upstream step failed. Work along the path:
- Test the actual target from Newt. The placeholder
curl -I http://目标IP:端口means replace the target IP/port, for example the NAS URL below. - Confirm the resource uses the correct Site.
- Verify HTTP versus HTTPS and upstream TLS settings.
- Check whether the backend binds only to
127.0.0.1. - Check LAN/server firewall access from the Newt host.
- Inspect Newt and VPS container logs.
# Newt 主机
ip route
curl -v http://192.168.1.20:5000/
sudo journalctl -u newt -n 200 --no-pager

# Pangolin VPS
cd /opt/pangolin
docker compose ps
docker compose logs --since=15m
In this diagnostic block, run the first commands on the Newt machine and the commands after the directory change on the VPS. localhost refers to the connector host/namespace, not automatically to the NAS. Check Docker addressing and routes when the application or connector is containerized.
sudo systemctl status newt --no-pager
sudo journalctl -u newt -n 200 --no-pager
sudo stat -c '%a %U:%G %n' /etc/newt/newt.env
Check:
- Correct Site ID/Secret, without extra spaces.
- Endpoint DNS pointing to the current VPS.
- Required UDP 51820 or the configured site port allowed by the provider.
- Home-network UDP restrictions and tunnel stability.
- Clock synchronization on both hosts.
- Server/Newt release compatibility.
Then check DNS, time and HTTPS:
getent ahosts pangolin.example.com
curl -I https://pangolin.example.com
timedatectl status
HTTPS reachability does not prove UDP works. Never paste complete secret-bearing startup commands or environment files into public support channels. If exposed, rotate Site credentials and update/restart the connector; deleting the message alone is insufficient.
dig +short A pangolin.example.com
dig +short AAAA pangolin.example.com
curl -I http://pangolin.example.com
sudo ss -lntp | grep -E ':(80|443)\b'

cd /opt/pangolin
docker compose logs --since=30m | grep -iE 'acme|certificate|challenge|error'
Confirm:
- A points to the current VPS.
- AAAA is present only when working.
- Provider and host firewalls allow the selected ACME method's ports, normally 80/443 here.
- No older proxy occupies those ports.
- CDN/proxy behavior does not interfere with validation.
- Correct domains and ACME contact email.
Fix the cause before retrying repeatedly; CA rate limits can turn repeated failures into a longer outage. DNS-validated wildcard certificates require their own DNS configuration rather than the HTTP checks above alone.
Check public domain, HTTPS, cookies and external identity-provider callback against the actual browser URL. Try a private window.
When a resource never asks for authentication:
- Confirm platform auth is enabled on the resource or inherited policy.
- Look for broad Allow/Bypass rules.
- Test logged out and from mobile data.
- Inspect priority and match conditions.
- Remove temporary bypass and retest denied access.
An already logged-in administrator may have cookies and privileges an ordinary visitor lacks. Test authorized, unauthorized and anonymous access separately.
- A/AAAA match real reachable VPS addresses.
- 80/TCP, 443/TCP, 51820/UDP and any client 21820/UDP exposure are deliberate.
- SSH is restricted and the provider console is available.
- Dashboard and resource certificates are valid.
- Newt environment file is 600 and credentials stay private.
- Backend access permits only necessary LAN sources.
- Public resources use authentication without permanent broad bypass.
- Share links expire and are revoked after use.
- VPS transfer and sustained bandwidth are sized to workload.
- Configuration, data and component versions are saved before updates.
- Backups are offsite and restoration has been tested.
- External tests cover login, resources and denied access.
The self-hosted quickstart needs a public-IP Linux server and a dashboard domain pointing to it. Home Newt connects outward, so the home connection normally needs neither public IPv4 nor application-port forwarding.
Public Resource traffic does, including downloads, photos and video. Verify Private Resource paths according to their connection mode and the actual architecture; do not assume the direct-peer behavior of another platform applies.
It may suit testing with swap and carefully limited load, but the current basic guide describes 2 GB RAM. Prefer 2 cores/2 GB/20 GB SSD with adequate transfer and sustained bandwidth; network capacity often limits large-file workloads first.
Pangolin has private and TCP/UDP capabilities, but browser SSO is not an authentication wrapper for an arbitrary bare protocol. Use private access/native authentication for administration and review game-specific UDP, latency, bandwidth and restrictions.
No. Any supported always-on host that can reach the target can serve as the connector: NAS, home server, small Linux machine or VM. VLAN isolation may need explicit routes and firewall permissions.
Managed ingress can reduce VPS operation when third-party hosting suits the workload. Pangolin offers control over the VPS and data path with responsibility for Docker, security, backups and upgrades. Outbound home tunnels do not automatically make published resources safe.
The ongoing work includes HTTPS, connector health, identities, resource permissions, temporary sharing, transfer monitoring and tested recovery. A light installation can start near 2 cores/2 GB/20 GB SSD with a workload-appropriate 1 TB transfer allowance; photo/file/video usage needs calculation rather than that default estimate.
Validate the dashboard, Site, Newt and one authenticated resource first. Add SMTP, external identity and more network features after that path is reliable. Keep version choices, access tests and recovery documentation current.